

A system has been created that takes different issues — climate change, pandemic risk, online misinformation — and converts them into financial risk scores. These scores flow into decisions that determine what can be insured, who can get loans, and… what is even allowed to exist, economically.
This represents yet another inversion: from governance as positive allocation (what to fund, what to build) to governance as constraint (what to stop, what to penalise). Central banks have become the de facto governors of economic activity through three financial choke points: capital requirements, collateral frameworks, and liquidity access. Control what is financeable and you control possibility.
In simple terms: ‘It’s the central banks, stupid’1.

Find me on Telegram:
The policies and frameworks behind this system are public, developed by central banks, regulators, and international institutions in response to identified risks, genuine… or modelled by the IIASA. What is less visible, however, is how tightly these now link risk assessment to economic viability.
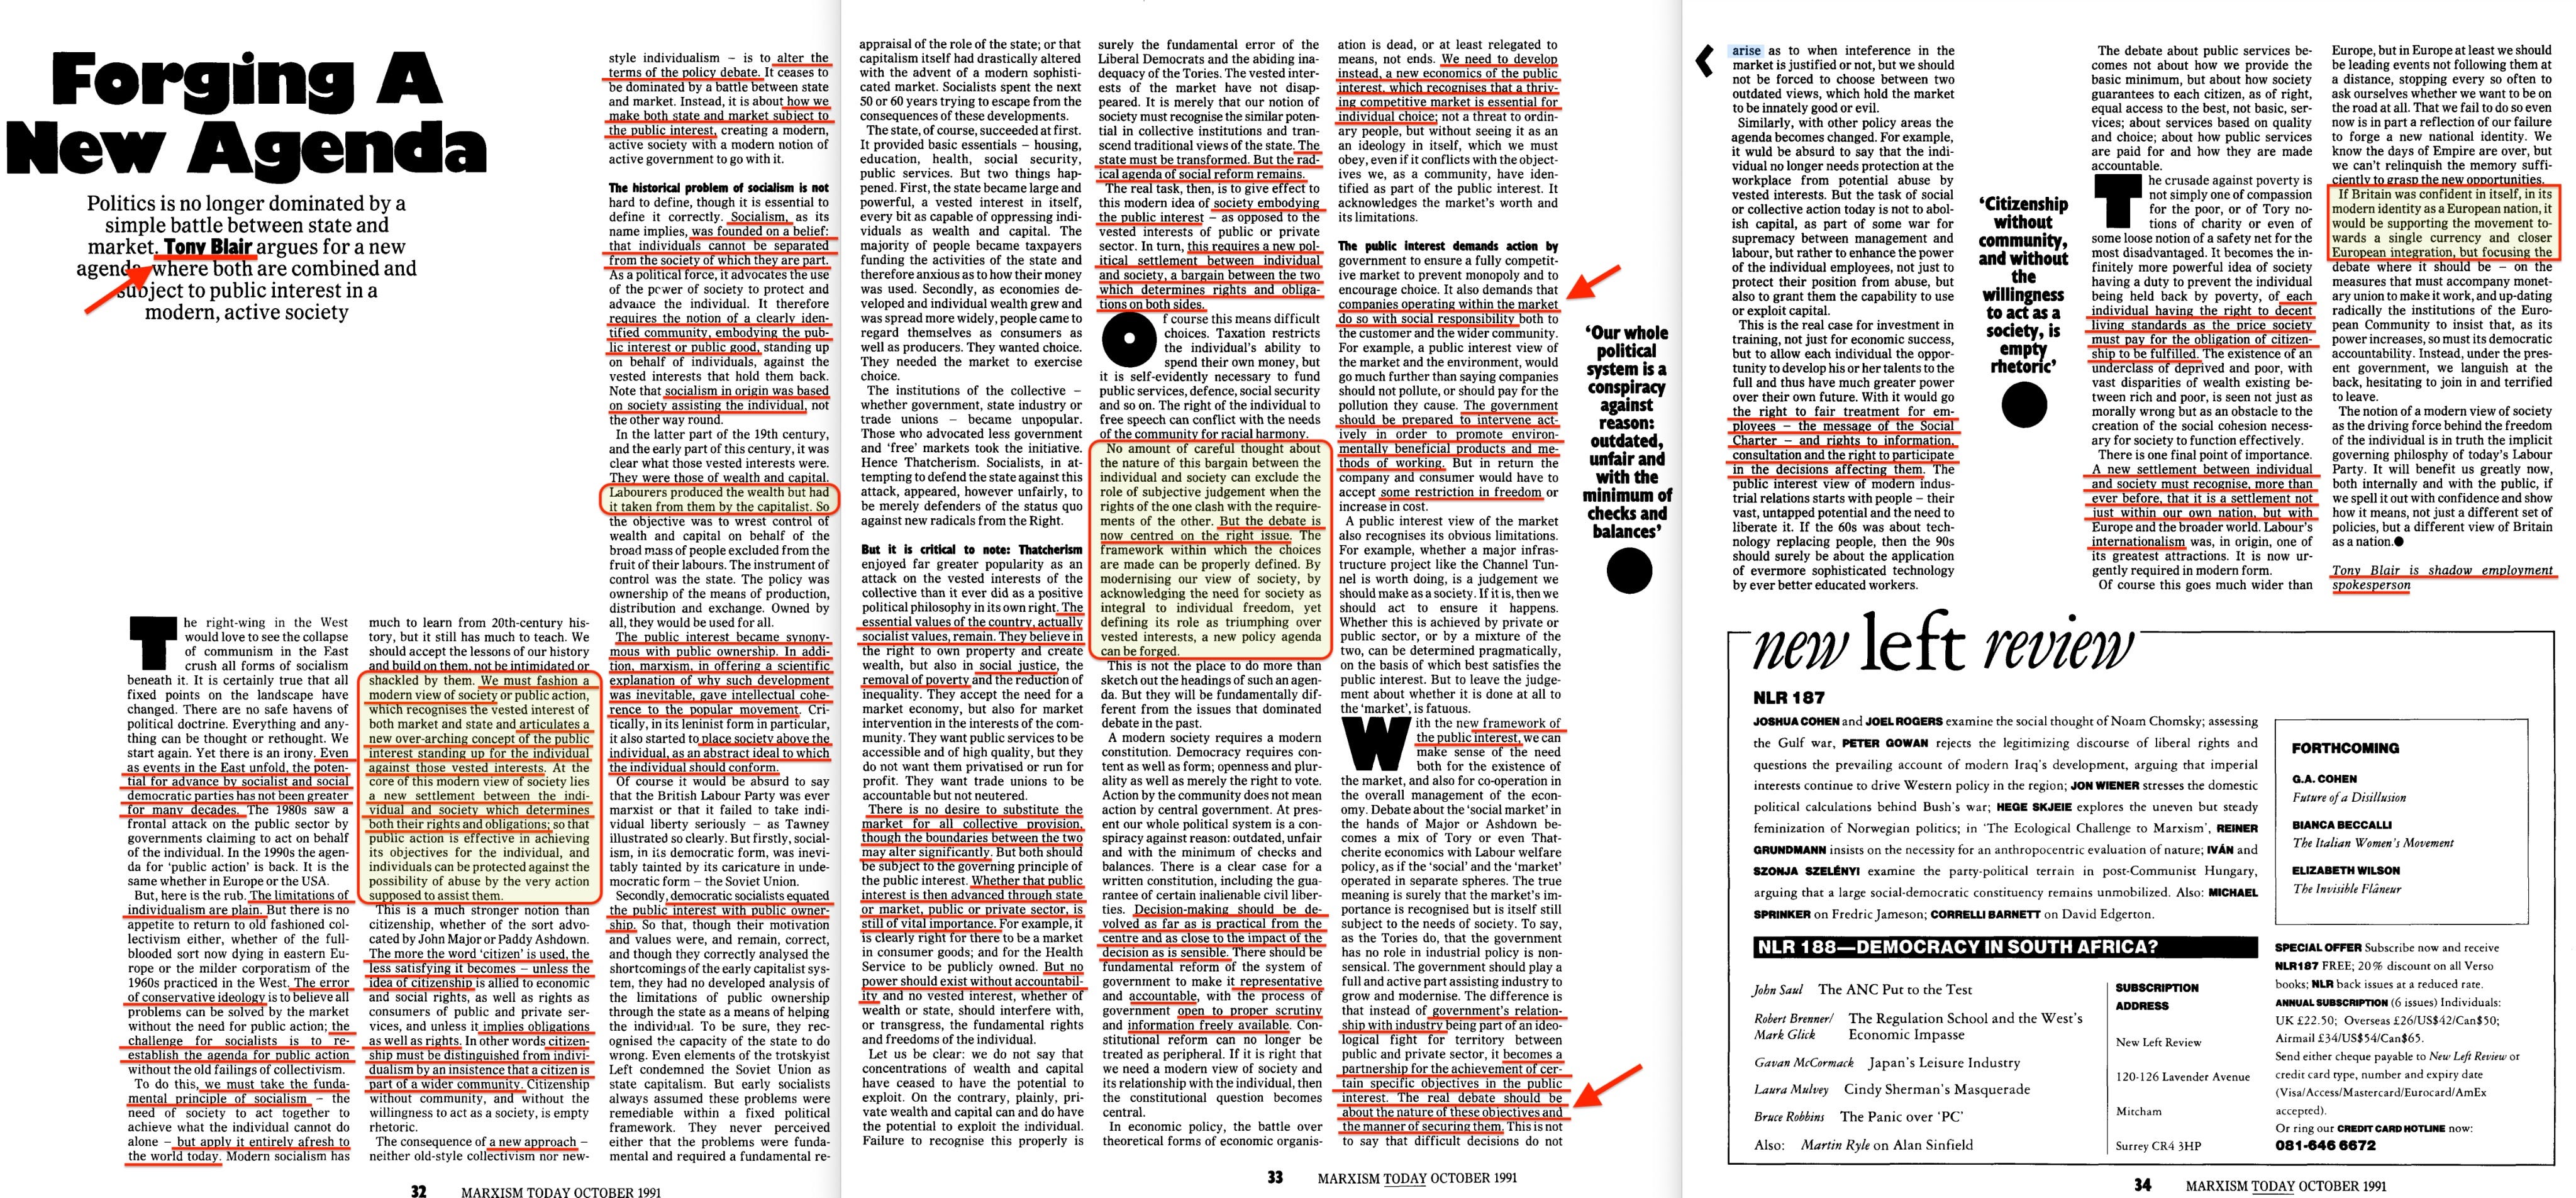
What’s also of interest is that Tony Blair in 1991 spoke of precisely a such system in his Marxism Today essay; ‘Forging a New Agenda’2.

The Old System
In 1961, Robert McNamara brought PPBS (Planning-Programming-Budgeting System) to the U.S. Department of Defense3. The logic was straightforward: define objectives, design programs to achieve them, and fund the programs with the best cost-benefit ratio. Governance became optimisation — given limited money, maximise goals. The approach spread to other agencies, corporations, and international development.
The key feature was positive allocation: deciding what to build, fund, and grow. JFK, however, turned it on his head, using it to force cuts to defence spending.


The Inversion
The emerging system uses similar machinery — scenarios, models, cost-benefit analysis — but flipped. Instead of ‘What should we fund?’ the question becomes ‘What must we constrain to stay within safe limits?’
The new logic works like this: define a ‘safe operating space’ for climate, public health, or the ‘information ecosystem’. Identify activities that breach that space, and score each activity’s contribution to systemic risk4. Apply financial penalties to high-risk activities. Monitor and tighten if risks persist5.
The central question shifts from what to build to what to stop.
Structurally, this inversion extends to the analytical method itself. Traditional PPBS relies on input-output analysis6: tracing how resources flow through sectors to produce goods and services. The inverted system relies on inverted input-output analysis — using the same economic matrices to trace risk instead of production. Standard input-output tables map production linkages — if this sector grows, which others grow with it. Risk matrices map harm linkages — if this activity continues, which systemic risks it amplifies. The same interdependence once captured for economic planning now gets captured for risk constraint via economics.
In simple terms: we used to ask ‘what makes the economy grow?’ Now the machinery asks ‘what makes the system look dangerous on our dashboards?’
Three Domains, One Financial Layer
Three domains are being wired into the same financial control layer.
Climate and Nature
The governing concept is ‘planetary boundaries’7 — nine Earth-system processes including climate, biodiversity, and freshwater that institutional frameworks questionably define as a ‘safe operating space’. Crossing these boundaries is characterised as ‘increasing the risk of systemic collapse’.
These risks are being translated into financial risk categories. The Network for Greening the Financial System (NGFS), comprising 148 central banks and supervisors, develops climate and nature-related financial risk frameworks8. The Bank for International Settlements has built ‘digital twin’ models that trace how physical climate damage transmits through company balance sheets to bank risk9.
The mechanism works through higher capital requirements for ‘brown’ assets, larger collateral haircuts for climate-risky assets, and climate stress tests that affect bank ratings10. For example, loans to coal-fired power projects attract higher capital charges and face stricter collateral treatment than loans to renewable projects under many transition frameworks. The ECB announced in July 2025 that starting in 2026, it will apply ‘climate factors’ to its collateral framework11 — assets from climate-risky sectors will be worth less as collateral, directly affecting financing costs. High environmental risk scores make activities progressively harder and more expensive to finance.
The BIS’s Project Viridis12 already prototypes the tools supervisors need for this. It gives them dashboards of ‘financed emissions’ at both system and institution level, consolidates reported and modeled emissions for major borrowers, and maps where those borrowers’ assets sit geographically so they can see how different carbon price paths or physical hazards would hit balance sheets. The infrastructure to link climate metrics to credit decisions is presently being built for supervisors as a standard platform.
The convergence extends across every major international standard-setter. The Basel Committee on Banking Supervision13 integrates climate into its prudential framework. The Financial Stability Board coordinates climate-related financial disclosure and systemic risk assessment globally14. And FATF — the Financial Action Task Force, originally created for anti-money-laundering — has expanded its scope to include environmental crimes: illegal logging, wildlife trafficking, illegal mining15. Once ‘environmental crime’ enters FATF’s remit, banks must treat it as a money-laundering predicate offense, triggering due diligence, suspicious activity reporting, and potential de-banking. The effect is to wire environmental enforcement into the same compliance machinery that already governs terrorism financing and sanctions. Every major node in international financial governance is now pointed at the same target.


Health and Biosecurity
The governing concept is ‘One Health’ — the WHO’s approach to ‘sustainably balance and optimize the health of people, animals and ecosystems’. One Health belongs to a family of integrative frameworks that share structural logic: the ‘Ecosystem Approach’ under the Convention on Biological Diversity, the ‘landscape approach’16 in land use and conservation, and emerging ‘global ethics’ frameworks17 such as the Earth Charter18 that position human interests as one consideration among others within planetary system management. In each, humans appear not as the subject of governance but as one variable within a larger system to be balanced and optimised.
In One Health19 specifically, humans appear as one population among others in disease-transmission models, alongside animal reservoirs. Human behaviours like farming practices, travel patterns, and population density become variables affecting outbreak probability.
These biological risks feed into financial frameworks through pandemic scenarios in central bank stress tests20, catastrophe modeling in insurance, and ‘operational resilience’ requirements for businesses. The mechanism produces higher capital charges for elevated pandemic risk, stricter insurance requirements, and lending restrictions for ‘biosecurity-noncompliant’ activities21.
Frameworks on the social, commercial, and environmental determinants of health22 extend this logic further. By treating health outcomes as the product of income, housing, education, marketing, and environmental exposure, they convert broad social and behavioural patterns into upstream risk factors. Once these determinants are quantified and attached to places, sectors, and populations, they can be fed directly into prudential models. What began as a call to address structural injustice becomes, in this context, a way of justifying differential financial treatment of groups on the basis of their modeled contribution to systemic risk.
The same integrative logic now applies to finance itself, you might call it ‘determinants of financeability’. Just as public health frameworks absorb housing, education, and environment into health risk, prudential frameworks now absorb climate behaviour, health compliance, information patterns, and social position into financial risk23. Every upstream factor becomes an input to a risk calculation that determines access to credit, insurance, and payment infrastructure24.
The pattern has precedent. NATO’s Committee of Three25 report in 1956 expanded the alliance’s mandate from military security to include political, economic, and social ‘determinants of security’ — absorbing non-military domains into security frameworks. The social determinants of health did the same for public health. Now the determinants of financeability do the same for economic participation. In each case, the move is structural: define your core variable broadly enough, and everything upstream becomes your legitimate concern.
The OECD provides the measurement layer. Its indicators26 — on governance27, economics28, environment29, well-being30, inequality31, trust32, and dozens of other domains — standardise the metrics that flow into risk models. Once an OECD indicator exists, it can be referenced in ESG frameworks, built into stress-test scenarios, and used to benchmark countries, sectors, and populations33. The indicator doesn’t just describe reality; it creates the categories through which reality becomes governable. Risk coefficients need something to measure, and the OECD supplies the ruler.
The result is a unified field theory of control: anything that affects any system the models care about becomes a factor in whether you can participate in the economy. The branding for this is ‘inclusive capitalism’34. Inclusive means everything is included in the risk models35 — climate, health, information, social position — and everyone is included in the system of financial governance. No one is left outside; no activity escapes measurement. The language of participation masks the reality of comprehensive capture.


Information
The UN’s Global Principles for Information Integrity36 frame misinformation as a threat to ‘the integrity of the information ecosystem’. UNESCO’s guidelines37 describe platforms as ‘ecosystems of misinformation’ requiring management. The WHO’s ‘infodemic management’ framework38 treats information overabundance as a public health risk.
Under the EU’s Digital Services Act39, large platforms must assess and mitigate ‘systemic risks’ including disinformation and threats to democratic processes. The mechanisms include algorithmic downranking, demonetisation, account suspensions, and fines up to 6% of global revenue. Financial ‘de-risking’ occurs when banks and payment processors deny services to entities deemed information risks.
In the information domain, the same logic shows up in proposals like the EU’s ‘chat control’ regulation40, which would require providers to scan private communications for prohibited content, including on end-to-end encrypted services. Formally it targets child abuse material; structurally it normalises bulk inspection of private speech as a condition of access to digital infrastructure. Once that capability exists, the only question is which risk categories the scanners are pointed at next.


Why Central Banks Are Decisive
Many institutions build risk frameworks. But central banks are unique because their assessments determine what gets financed cheaply, what gets financed at punitive rates, and what stops being financeable altogether.
Alongside this, development banks and climate finance institutions continue to channel positive funding into activities classified as aligned41 with transition and sustainability goals42. Central banks increasingly provide the inverse function: by adjusting risk weights, collateral treatment, and lending conditions, they make certain activities progressively easier, and others progressively harder, to finance43. The result is a two-handed system — one hand allocating toward approved activities, the other withdrawing from disapproved ones.
Central banks control the binding constraints44: capital rules dictating how much banks must hold against different asset types, collateral frameworks determining which assets are acceptable and at what discounts, liquidity access deciding who gets emergency support, and payment infrastructure including potential Central Bank Digital Currencies45.
Over the last decade, that prudential leverage has been paired with a quiet push to ‘coordinate’ fiscal and monetary policy. In reports and working groups, central banks and their policy allies now argue for formal committees where treasuries, central banks, and unelected ‘stakeholder’ commissions jointly set the overall stance of policy in the name of climate targets, inequality, and ‘fiscal sustainability’46. On paper this is coordination; in practice it gives the institution that controls the bond market and lender-of-last-resort function a de facto veto over budgets. Proposals like the UK’s In Tandem framework simply make explicit what the Truss episode already showed in practice47: a government that ignores its central bank can be disciplined not by a vote, but by a spike in yields48.
Once risks from any domain are embedded in these models, every economic activity gets shadowed by one question: How does this affect the bank’s risk assessment? Over time, those risk-based decisions feed back into the data: sectors that become harder to finance shrink or restructure, and their changing profiles are then used to update the risk models.
Central banks don’t need to ban coal plants. They make them unfinanceable by raising capital requirements49, excluding assets from favorable collateral treatment, and building risks into stress tests. The activity doesn’t disappear because it was outlawed. It disappears because it couldn’t get financed.


The Documentary Record
The architecture described here is not speculative. The institutions publish their frameworks openly; the question is whether anyone reads them.
The BIS and Bank of France’s 2020 report The Green Swan50 states that ‘the immediate and system-wide transition required to fight climate change could have far-reaching effects potentially affecting every single agent in the economy and every single asset price’ and that ‘Climate-related risks could therefore threaten central banks’ mandates of price and financial stability, but also our socio-economic systems at large’. It calls for central banks to enhance climate risk monitoring, develop new methodologies, and study prudential regulation for climate-related stability risks — meaning central banks will determine which economic activities remain viable.
The NGFS Conceptual Framework51 provides ‘a conceptual framework to guide action by central banks and supervisors... to highlight what is material from a microprudential, macroprudential, or macroeconomic perspective’ — in plain terms, what counts as a risk that regulators should act on.
In July 2025, the ECB announced that from 2026, climate factors will be incorporated into its collateral framework52. Assets from climate-risky sectors will receive larger haircuts, directly affecting financing costs53. But collateral treatment is just one lever. Climate risk is being wired into multiple mechanisms simultaneously: collateral haircuts that reduce what banks can borrow against climate-exposed assets, capital requirements that force banks to hold more reserves against ‘brown’ exposures, stress tests that penalise portfolios with high transition risk, and supervisory expectations that pressure banks to produce credible ‘transition plans’. Each mechanism points the same direction: higher costs for assets not considered ‘green’. Separately, any one might be dismissed as technical adjustment; together, they form a coordinated system for making entire sectors progressively unfinanceable.
Meanwhile, the UN’s Global Principles for Information Integrity treat unrestricted speech as a risk to ‘the integrity of the information ecosystem’ — a problem to be managed, not a right to be protected. These are not proposals under debate. They are operating frameworks already being implemented54.


Humans as Variables
In traditional governance, humans are subjects — beings whose welfare government serves. The ‘democratically cosmopolitan’ UN Declaration of Human Rights55 describes humans as ‘endowed with reason and conscience’.
Meanwhile, your consumption profile is abstracted into climate risk parameters that feed ECB collateral treatment and bank capital models. Your health behaviours and compliance patterns are folded into pandemic risk scenarios and amplification scores in WHO-style preparedness models. Your speech and sharing patterns help train the datasets behind misinformation and toxicity indices used to police the information ecosystem.
The bait-and-switch is structural: human rights language becomes the vehicle for human risk scoring. The moment ‘inherent dignity’ meets central bank and governance models, the person is recast as a vector in someone else’s optimisation problem. It is dehumanisation by spreadsheet.
In this system, humans appear differently in each domain. In climate frameworks, humans are characterised as the primary drivers of boundary transgression56. In health frameworks, humans appear as host populations and vectors in disease ecology57 — one column in the transmission matrix. In information frameworks, humans are vectors whose beliefs and communications support or undermine system objectives58. Across all three, humans function as optimisation variables to be adjusted to bring the system within designated operating limits.
This is far from the promise of equity and care — this is the most explicit dehumanisation of humans possible.


Group-Relative Governance
Risk models rarely work on atomised individuals. They work on sectors, regions, income brackets, behavioural clusters, and demographic categories59. If the system manages humanity as a risk factor within planetary systems, the operational question becomes: which groups pose how much risk to which system goals?
When objectives include staying within carbon budgets, minimising outbreak risk, and preserving ‘information integrity’, models will identify unequal contributions and unequal risk profiles between groups. Prudential logic then implies that risk-weighted treatment should differ accordingly60.
In climate frameworks, groups differentiate by emissions and land footprint61. High-consumption urban professionals versus low-consumption rural populations. Industrialised economies versus resource-extractive ones. Workforces in aviation, fossil fuels, or meat production. Prudential logic treats some groups’ lifestyles and jobs as higher transition risk62, their sectors’ assets as more likely to become stranded, their economic futures as more expendable in the portfolio. This is financial redlining by compliance score at group level — the establishment of a carbon class.
The determinants of health, One Health and pandemic preparedness frameworks are already group-based. High-density urban areas versus low-density rural. Countries classified as zoonotic hotspots. Communities identified as vaccine-hesitant behavioural clusters. Risk matrices classify which populations are more likely to generate spillover, which groups amplify transmission, which clusters resist compliance63. Financial and regulatory responses then differ: stricter conditions on farms, markets, or travel from certain regions; harder insurance and credit terms for certain agriculture or settlement patterns; more aggressive interventions for non-compliant populations64.
In information frameworks, group-relative management is the operating logic. Communities with high rates of flagged content, or lack of trust in institutions. Political factions labeled extremist or anti-science. Platforms and regulators distinguish vulnerable audiences from superspreader communities, trusted partners from repeat offenders. Risk logic implies content from some groups needs proactive throttling, some groups’ economic infrastructure is higher risk, therefore they receive less visibility, less financial connectivity, more monitoring. Once wired into payment rails and banking reputational-risk policies, group-level information risk becomes group-level economic risk, and a full social credit system is merely a step away.
The categories through which these group differences are mapped did not originate in risk management. Intersectionality and critical theory, developed from the 1930s through the 1980s as emancipatory frameworks for analysing how multiple axes of oppression combine, now supply the taxonomies65. Global governance discourse routinely invokes vulnerable and marginalised groups, intersectional harms, systemic discrimination, and social cohesion66. This language appears in ESG social metrics, human rights impact assessments, UN ‘Leave No One Behind’ documentation, platform trust-and-safety frameworks, and public health equity panels.
Intersectionality provides a coordinate system for classifying human groups by their relative positions in a harm-and-power landscape67. Risk management has adopted that same coordinate system for classifying groups by their relative risk-and-impact profiles68. This was not incidental. The same academic networks, foundations, and policy entrepreneurs that developed these frameworks actively worked to embed them in international institutions, corporate governance standards, and regulatory guidance. The axes remain the same — race, gender, class, religion, region — but they now serve dual purposes. Critical theory uses these categories to argue for redistribution and emancipation69. Prudential governance uses them to identify political risk, volatility, compliance risk, and reputational risk70. The categories moved from seminar rooms to UN working groups to ESG rating agencies to central bank risk frameworks through deliberate institutional effort, not conceptual accident.
The same categories once used to argue ‘these groups are oppressed’ are now being used to say ‘these groups are risky’.
The result is a dual function. On the front end, the language serves an ethical purpose: ‘protect vulnerable and marginalised communities’. On the back end, it serves a prudential purpose: these configurations of grievance, identity, and inequality constitute social and political instability risk, which must be monitored and mitigated. A grammar of justice becomes a grammar of control.
Contemporary global governance often draws on hierarchical ethical frameworks that present ‘more systemic’ or ‘more inclusive’ perspectives as ‘morally superior’71 — wider circles of concern carrying both the right and the duty to manage narrower ones72. The key legitimating concept is interdependence: because climate, health, economy, and information are interconnected, governance must be integrated73; because local actions have systemic effects, local autonomy must yield to systemic management; because everything affects everything else, everything becomes a legitimate object of coordinated control.
Interdependence also implies feedback — and feedback is the foundation of cybernetics74. Once systems are understood as interdependent and continuously feeding back into one another, they become candidates for adaptive management: monitor, model, adjust, repeat75. The control system never reaches a final state; it continuously recalibrates based on observed deviation from target parameters76.
Instead of visible laws that change occasionally, you get invisible thresholds that move continuously — and increasingly automatically.
This creates a structural accountability gap. Traditional legislation happens at discrete moments, with debate, votes, and the possibility of repeal. Adaptive management happens continuously, through technical adjustments to models, parameters, and risk weights. There is no single decision point to contest, no vote to oppose, no law to repeal — just an evolving set of scores and thresholds maintained by expert bodies insulated from electoral pressure.
The mechanism operates through quiet recalibration. The ECB does not declare ‘we are banning fossil fuels’; it might raise a climate risk factor in its collateral framework — say, from 1.2 to 1.5. The NGFS does not vote to defund carbon-intensive agriculture; it updates scenario parameters that flow into bank stress tests. By the time citizens notice that their local fuel supplier cannot get loans or their farm faces punitive insurance terms, the system has already reconfigured economic reality. The decision was never announced because, formally, no decision was made — only a technical adjustment to a model.
The democratic deficit is not a bug but a feature: the system is designed to be responsive to data — not the public. And because the models can always identify new boundaries to protect — emerging pathogens, novel pollutants, fresh categories of harmful speech — the emergency framing is permanent. There is no point at which the system declares victory and relaxes. The boundary conditions simply migrate, and the constraints follow.
Risk models are self-reinforcing. Shrink coal and the models register success, which justifies tightening carbon budgets, which strangles steel and aviation. Crush bushmeat markets and the system claims victory against zoonotic risk, justifying the expansion of ‘hotspot’ designations which in turn restricts rural farming. Silence flagged speech and ‘information ecosystem integrity’ improves, which justifies new speech boundaries, in turn throttles dissent. Each success becomes the evidence base for the next expansion. In the story the institutions tell themselves, they don’t choose to raise climate risk factors; their models demand it. The system isn’t broken — it is working as designed.
In practice, these hierarchies translate into risk-weighted management of groups: those classified as less aligned with systemic goals are treated as higher risk and subjected to tighter financial and behavioural constraints. The ethics story is what makes the control system feel not only necessary but morally obligatory.


Cross-Domain Reinforcement
The three domains form a coupled system. Climate disruption is supposedly linked to pandemic risk through habitat loss driving pathogen emergence77. Per the Pandemic Treaty, that can trigger health controls including lockdowns, mandates, and surveillance. In turn, those are alleged to generate information turbulence through resistance and competing narratives. This supposedly justifies information controls like content moderation and counter-disinformation campaigns, as we experienced during Covid. Yet, information controls can reinforce climate constraints, for example when criticism is categorised as ‘climate denial’78.
Each layer’s enforcement depends on control in the others. Long-term pandemic controls require limiting debate about costs and effectiveness. Stringent climate controls require limiting questioning of models and targets. Information controls require limiting organisation outside monitored platforms.
The architecture of control only moves in one direction.


Surveillance and Anticipatory Governance
This architecture requires continuous, comprehensive data collection to function. Risk models need continuous inputs across all three domains: emissions and resource use, movement and health status, information consumption and production. The more granular the risk pricing, the more granular the surveillance required to feed the models79.
Digital twins — virtual models of physical systems — are being built precisely to close the loop between real-time data and prudential decisions. BIS Innovation Hub projects80 on climate and financial stability already integrate high-frequency environmental, economic, and market data into scenario tools used by supervisors. Project Viridis81, built by the BIS Innovation Hub and the Monetary Authority of Singapore, is explicitly framed as a ‘climate risk platform for financial authorities’ — an integrated data and analytics system that sits on top of banks’ regulatory reports, scrapes climate-relevant information from corporate disclosures with NLP, and lets supervisors run climate scenarios across sectors and geographies from a single console. Its modular design means new metrics and standards can simply be plugged in as they emerge. The same logic extends to modeling pandemic spread, information cascades, or behavioural patterns. These tools make governance anticipatory82: acting on predicted future risk rather than past behaviour.
As sensor networks and IoT devices proliferate — from industrial equipment to farm fields — the technical capacity exists to feed those data streams directly into risk engines. Your John Deere isn’t just plowing fields; it’s streaming soil and yield data into systems that can feed the climate-risk dashboards banks and supervisors use to set your loan terms before you harvest83. In that configuration, your farm’s soil moisture sensors or your factory’s energy meters would not just support better agronomy or maintenance — they would update the risk scores that determine your financing before you plant or expand. This isn’t anticipatory governance as future possibility; it’s control already operating in the space between intention and action.
Within the ecosystem approach84 and related frameworks, humans are weighted relative to animals, ecosystems, and planetary processes in risk calculations. Risk models incorporate these weightings when calculating acceptable activity levels. A farming practice might score high on productivity but be penalised for zoonotic risk, antimicrobial resistance contribution, and emissions intensity.
The result is anticipatory governance priced in through risk management85. Constraints don’t arrive as laws debated in public, but as risk scores updated in models, flowing through to capital requirements, collateral treatment, and transaction conditions. Governance happens before the act, embedded in what is economically possible rather than openly legislated.


Questions of Necessity and Legitimacy
Proponents argue these frameworks respond to systemic risks that don’t respect borders and require coordinated action.
Critics argue that ‘emergency’ framing has historically justified permanent power expansion, that models defining ‘safe spaces’ embed contestable values, that centralised control creates single points of failure, and that top-down management has a poor track record with complex systems. More fundamentally, they argue this is not ultimately about climate or pandemics or misinformation — it is about creating an unchallengeable governance layer. The moment any human activity gets mapped to systemic risk in central bank models, it becomes subject to financial constraint without political process. The specific emergency is interchangeable; the architecture of control is constant. The ‘meta-crises’ is born86.
On legitimacy: what counts as ‘safe’ or ‘misinformation’ involves values, not just technical criteria — but who decides? Key decisions happen in transnational networks like the BIS, NGFS, and WHO, largely insulated from democratic input. Most people don’t know this architecture exists, as control operates through technical mechanisms. And once financial systems restructure around these scores, reversal becomes extremely costly.
These frameworks are typically shaped in working groups that combine central banks, financial regulators, international organisations, large financial institutions, and selected NGOs or experts, rather than through direct parliamentary processes.
The 2024 US election illustrates how little electoral outcomes matter to the underlying machinery. The same central banks still sit in the NGFS, the same prudential committees still run climate scenarios, the same supervisors still integrate those scenarios into stress tests and capital models. Whether voters chose red or blue, the framework treating climate, health, and information as systemic risks did not come up for a vote — and it did not pause for reconsideration. That is the design: it functions across administrations and beyond electoral cycles, tightening and extending itself through technocratic bodies that are structurally insulated from politics.
Even legal challenge may come too late. Imagine a constitutional court, a few years from now, ruling that parts of the ECB’s climate framework overstepped its mandate. By that point, banks will have already repriced trillions in assets against those parameters. Entire sectors will have restructured or disappeared. Investment patterns will have shifted irreversibly. You can strike the rule from the legal register, but you cannot un-bake it from balance sheets. The system is designed to create facts on the ground faster than democratic institutions can respond — and to make reversal economically unthinkable even when it becomes legally possible.


CBDCs as Potential Endpoint
Currently the system operates at the wholesale level. Central banks and regulators set conditions for banks, insurers, and payment providers. A coal company’s loan is more expensive than a solar farm’s. A media company flagged as high reputational risk finds banking relationships fragile. A meat producer in a high zoonotic risk zone faces stricter lending conditions. But individuals feel this only indirectly — in what’s available, at what price, on what terms.
CBDCs don’t invent risk-based governance; they change its granularity and point of application. Without CBDCs, the pipeline runs: central bank and regulators → banks, insurers, platforms → your options and prices. With programmable CBDCs, in the strong version, you could have: central bank or public authority → direct conditions on categories of transactions. Programmable CBDCs don’t create the governance logic; they move it from the balance sheets of banks into the fabric of everyday transactions, where model-driven constraints are felt directly at the point of sale.
The same institutions that build climate and financial stability scenarios are already experimenting with CBDC architectures, digital twins, and granular transaction data87. In public, these pilots are framed as efforts to improve efficiency or inclusion. In practice, they demonstrate how quickly authorities could move from portfolio-level risk limits to behaviour-level throttling: adjusting transaction permissions in specific sectors, regions, or time windows in response to modeled ‘civil unrest’ or ‘misinformation’ risk. The logic is identical to climate scenario analysis, simply applied to people instead of portfolios.
Read concretely: the Fed’s Hamilton Phase 2 pilot88 isn’t just about digital dollars; functionally, it’s a test of how fast retail payments can be segmented, throttled, and geofenced in real time. BIS Innovation Hub papers already model how targeted constraints on specific sectors or regions feed through to liquidity and prices over a few days’ time. This isn’t hypothetical architecture — it’s behavioural conditioning wired directly into the payment rails.
Two levers are available. The first is pricing risk — making certain behaviours more expensive through fees, rates, or haircuts. This can be done through existing intermediaries, just more crudely. The second is permissioning risk — allowing, blocking, or capping transactions based on risk conditions. This becomes much more direct when money is issued as a programmable ledger entry and every transaction passes through a rules engine that can reference risk scores.
In the current system, risk-based constraints run at the level of institutions and sectors: this portfolio is too risky, so increase capital requirements. With CBDCs, those constraints could run at the level of behaviour and transactions: this kind of transaction, in this context, is too risky, so apply a fee, friction, or block for that specific spend.
The transition from wholesale to retail makes the consequences personal. Today, a coal company is denied loans; tomorrow, a CBDC blocks your gas station purchase. Today, a media company loses banking relationships; tomorrow, your ‘information risk score’ spikes and your payment accounts freeze.
The kill zone emerges where financial and behavioural control intersect. Protest climate policy and your civil unrest risk score jumps, loan rates spike, you lose your home. Organise resistance and your community is labeled a superspreader cluster, payment rails cut you off. The machinery converts dissent into financial suicide. No police, no courts, no visible coercion — just a quiet adjustment to your risk parameters and the economic walls close in.
Not all CBDC designs will go that far, and much depends on political choices and legal constraints. But if the logic runs from planetary boundaries to risk matrices to prudential rules to digital rails, then programmable CBDCs are the natural infrastructure for per-transaction89, risk-conditioned money90.


Implications
Risk-management governance treats novelty as a threat. The unknown is unmodeled; the unprecedented is uncontrolled. A system optimised for stability within predefined bounds is structurally hostile to creative destruction91.
The architecture tends toward stratification. The risk-compliant — those with low footprints, high health compliance, and platform-approved views — get good credit, low rates, and full access. The risk-flagged get poor credit, high rates, and restrictions. This produces financial redlining by compliance score. And that’s even before we mix in ‘original sin’ factors such as ‘intergenerational equity’92.
How this shows up in ordinary life:
Your bank says a certain line of work is ‘too risky’ to lend into, even though you’ve never missed a payment. Your insurance premiums spike because of a postcode’s ‘climate’ or ‘health’ profile, not because of anything you’ve personally done. A payment processor quietly drops independent media or small churches because of ‘reputational risk’ tied to information integrity rules. A future CBDC pilot caps how much fuel or meat can be bought in a region during a ‘climate emergency’ or ‘health crisis’.
Freedom within safe boundaries means choosing among approved options, expressing permitted opinions, and engaging in financeable activities. The critical choices — what boundaries exist, what risks matter — are made by institutions outside democratic control.
Once risk scores are embedded in prudential frameworks and transaction rails, they don’t just constrain what can be financed. They also become inputs into new financial products. The same indicators used to penalise non-compliance can be used to reward and monetise compliance — sustainability-linked bonds that step coupons based on firm-level ESG metrics point toward behaviour-linked bonds that step coupons based on population-level KPIs. At that point, prudential risk management of humanity turns into something further: the financialisation of compliance itself.
Ethical behaviour stops being an expression of human agency or communal self-rule and becomes a performance obligation owed upward to creditors.
An open question is whether similar tools could even be designed with explicit democratic oversight and clear limits, or whether the logic of risk-based financial governance makes that impossible to achieve. Until that question is faced honestly, money will remain the hidden hand of global governance — quietly deciding which futures are still financeable… and which are not.
What we are witnessing is, in essence, the fulfillment of Moses Hess’s nineteenth-century vision: the reform of economics to serve an agenda of social justice. Hess argued that transforming the economic base was the route to transforming society. Tony Blair’s 1991 essay ‘Forging a New Agenda’ in Marxism Today updated the same logic for the post-Cold War moment93 — moving beyond traditional socialism while retaining the goal of using economic levers for social transformation.
The contemporary version does exactly this — but routes the transformation through risk models, prudential frameworks, and central bank balance sheets rather than through democratic politics. The goals are framed as planetary survival, public health, and social equity; the method is the quiet re-engineering of what money will and will not finance. It is socialism by spreadsheet, implemented not through revolution but through collateral haircuts controlled by central banks.
Consequently, I can think of no better title for this essay:
‘It’s the central banks, stupid’


5th point of communist manifesto
It seems western civilization is on the liability side of the Central Bankers' ledger...